· Marc Morel · Architecture · 4 min read
Gray patterns: Staying on the path when the standard doesn't fit
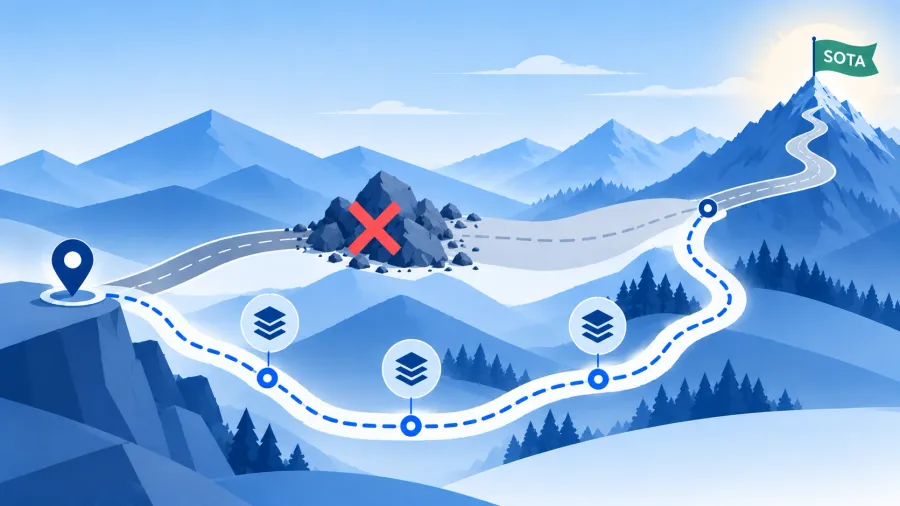
Architecture standards usually offer two outcomes: comply, or get an exception. Real systems need a third option: a sanctioned, bounded deviation that keeps the State-of-the-Art (SOTA) target within reach.
Most architecture teams eventually publish their standards: event-driven integration, delegated authentication, versioned contracts, built-in observability. Good standards. Then reality shows up.
A core system only produces flat files. A vendor package, bought for its business value, supports nothing but static API keys. A partner dictates its own protocol. The standard doesn’t fit, and not because anyone cut corners. There is a legitimate reason.
At that point, most governance models offer two options:
- Comply anyway. Cost and delay grow out of proportion, and sometimes the project stalls. The standard loses credibility with the teams it is meant to serve.
- Grant an exception. The team gets permission to deviate, decided case by case, with no shared direction. Each team builds its own workaround, the gap leaks into contracts, and nobody can say how far the landscape has drifted from the target.
Over time, exceptions tend to become the real architecture, and the standards end up describing a system that doesn’t exist.
I think we are missing a third category: the gray pattern.
What a gray pattern is
A gray pattern is a pre-approved, documented variant of a standard. It accepts a local gap under two conditions: it preserves the intent of the standard, and it preserves the path to the target.
The core idea is simple: pay for the deviation at the boundary, not in the contract. Contain the gap in a seam (an adapter, an anti-corruption layer, a gateway) so the rest of the landscape consumes a compliant contract. The legacy system deviates. Its consumers don’t.
Two examples.
A batch-only core system. The standard is event-driven integration, with schemas in a registry. The core system can only produce a nightly export. Exposing that file directly would spread the constraint to every consumer. The gray pattern: an adapter reads the export, computes the deltas, and publishes events in the target format. Consumers are compliant today, and the degraded latency is documented. When the core system is replaced, only the adapter goes away.
A vendor package with static keys. The standard is OAuth 2 with audience-restricted tokens. The package only accepts a static API key. The gray pattern: a gateway validates target tokens on the consumer side and swaps in the key on the vendor side. The key lives in a vault, gets rotated, and every access is logged. The gap is real, but it is contained, controlled, and reversible.
Borrowed, not invented
None of this is new. PCI DSS has long formalized compensating controls: when a requirement can’t be met for a legitimate reason, you demonstrate an alternative control that covers the same risk, and you review it regularly.
Gray patterns bring that logic to architecture. We don’t deviate from a standard. We deviate from one implementation of it, and we show that the risk it addressed is still addressed. For regulated organizations, this is also the language auditors and DORA expect: a gap that is identified, justified, compensated, and tracked.
Anatomy of a gray pattern
Six fields. Each one carries weight.
- Legitimate trigger. The situations that justify it: legacy that can’t change, a vendor constraint, an explicit business-value decision.
- Invariants. What stays non-negotiable (security, traceability, data residency) and what can flex (protocol, format, technology).
- Compensating control. How the risk behind the standard stays covered.
- Path to target. The migration seam, and what gets removed once the constraint goes away.
- Expiry and owner. A review date, and a named person accountable for it.
- Measured distance. A fitness function or debt indicator that keeps the gap visible.
Without a path to target, a pattern isn’t gray. It’s a well-documented deviation.
The risk: normalizing deviance
Studying the Challenger disaster, sociologist Diane Vaughan described how a deviation tolerated once becomes the new implicit norm. Gray patterns are exposed to this by design, because they make deviation comfortable. Three guardrails help:
- Mandatory expiry. Renewal is explicit and justified.
- Strict scope. A gray pattern applies to the context it describes, never by analogy.
- Tracked adoption. If a gray pattern shows up everywhere, the standard is probably miscalibrated. The fix is to revisit the standard, not to keep issuing variants.
That last point is the one I value most. Gray patterns act as a sensor: they surface the gap between the standards and the field, where binary exceptions tend to hide it.
What changes
- For delivery teams: a ready answer instead of a review board.
- For architecture: debt that is contained, dated, and measured.
- For the standards themselves: a feedback loop that keeps them grounded.
State of the art isn’t a state we declare. It’s a direction we hold. Good standards tell teams where to go, and how to keep moving when the road is blocked.